
Last month, we covered a new SMS phishing scam specifically targeting iPhone users. The idea behind the scheme is to encourage the recipient to respond to a text in order to activate a link, which would then be clicked, either deliberately or inadvertently, and activate an element of malware.
Messages in iOS 18 have a functionality that deactivates hyperlinks when receiving a text from a number that is not in your contact list. This additional piece of security makes you difficult for the crooks to encourage you to click on their links – unless you answer, which unlocks the link.
The idea is that the original text informs you to answer with something as simple as a y or n, so the link will become clickable. It is generally a question or a kind of withdrawal thing to make you answer. But the one I received on Thursday was neither intelligent nor delicate.
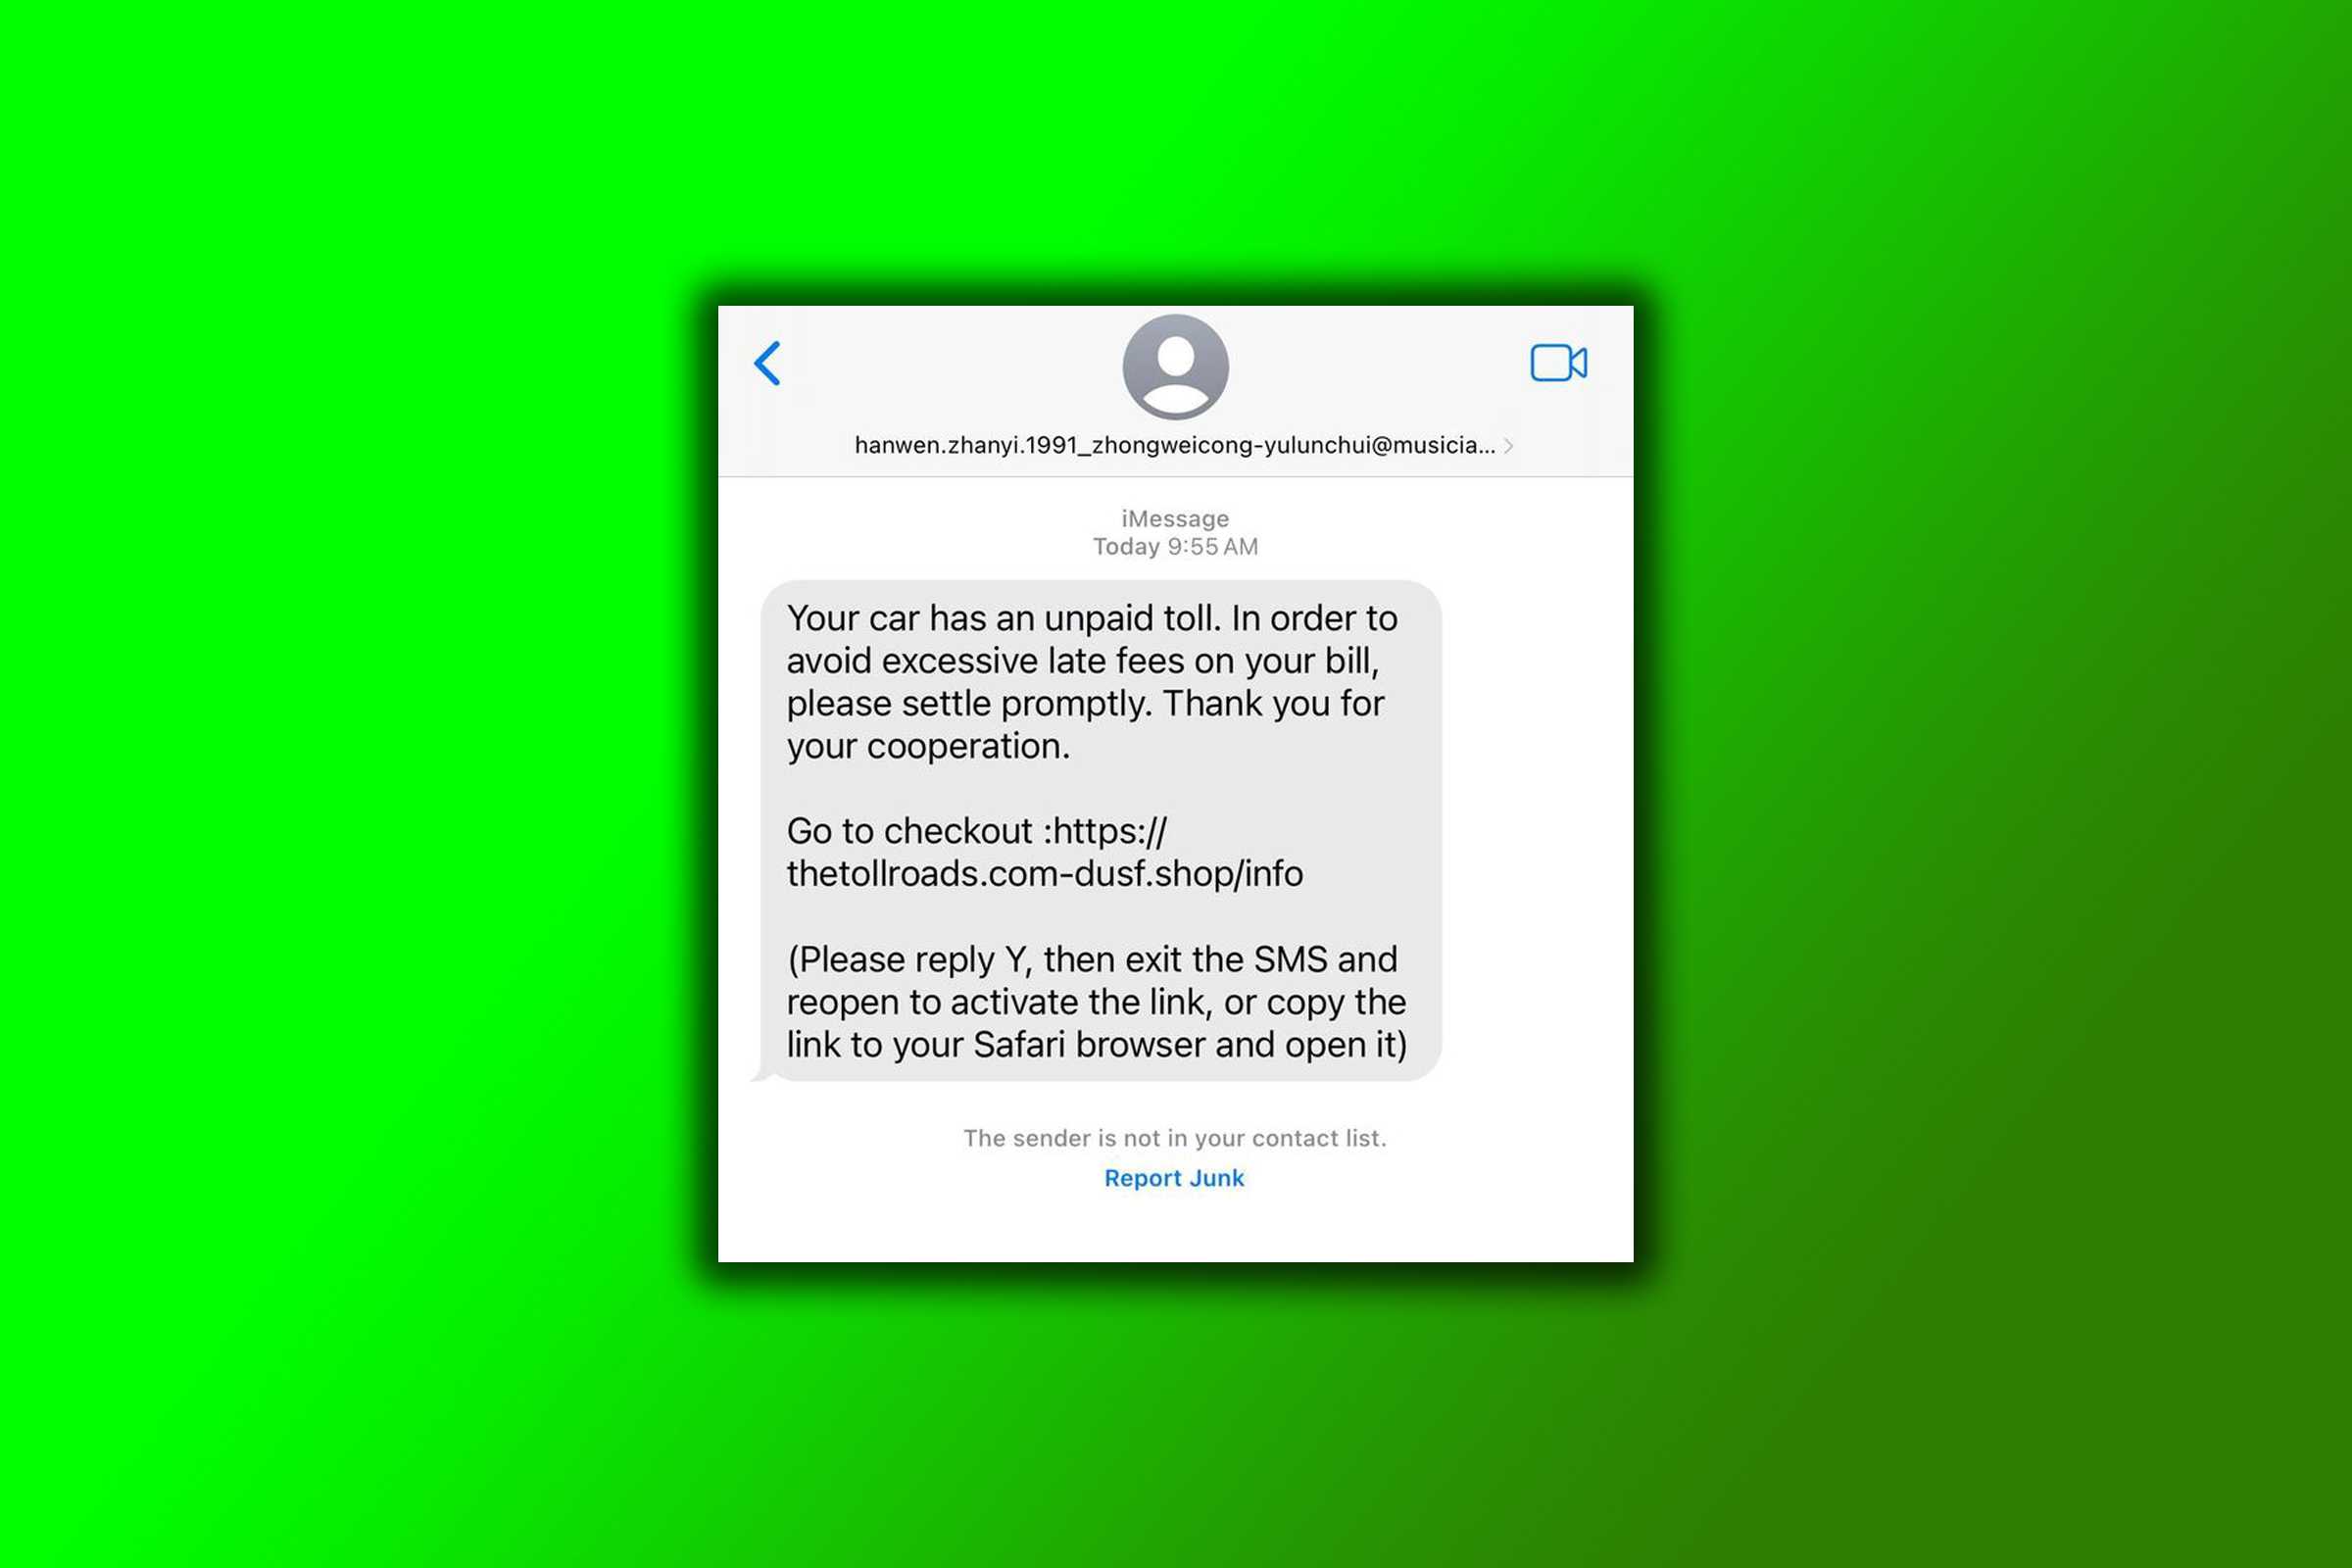
The first opinion was the name of the sender, which was too long to even display on the screen: [email protected]. The second index was the text of the message, which told me that my car had an unpaid toll and asked me to “settle properly” to avoid “excessive late costs”.
Foundry
After all, this scary text was a web address without hyperlink because the number was unknown. Instead of trying to make me answer, however, the rest of the message said: “Please answer Y, then leave SMS and rouve to activate the link, or copy the link to your Safari browser and open it.”
It is about as obvious that an attempt by Smirs can get it. I guess it is possible that a user without distrust can involuntarily follow these instructions and open their phone to malicious software, but it is just an advertisement for the excellent security measures of Apple to avoid attacks even before you can to start.
Sorry, [email protected], maybe next time, try an Android user.


